News feed

What attackers are doing, what it means for you, and how Bastion handles it

What we test for

PHP/CVE-2026-109618, CVE-2026-109619

PHP2Shell

Two flaws in PHP's core can allow unauthenticated remote code execution. Fixed in 8.5.12, 8.4.27, 8.3.36 and 8.2.35.

Patching is the easy half. Attempts began four days before disclosure, so check what was planted, not just the version.
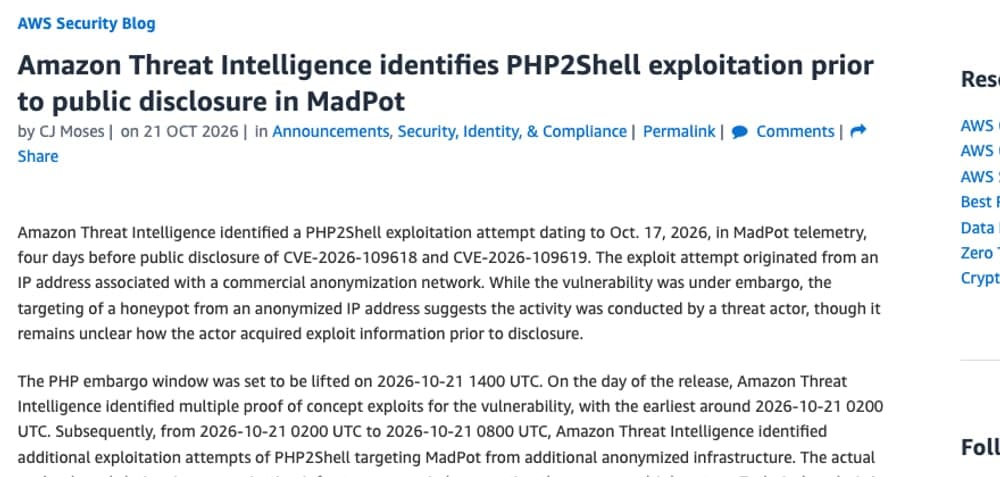
Coverage of PHP2Shell

Read on AWS

With Bastion

We find every PHP answering from outside, replicas and old images included, and flag the ones still exposed once the fix ships. After you patch, we check again.
WordPress core/CVE-2026-119977

The WordPress upgrade window

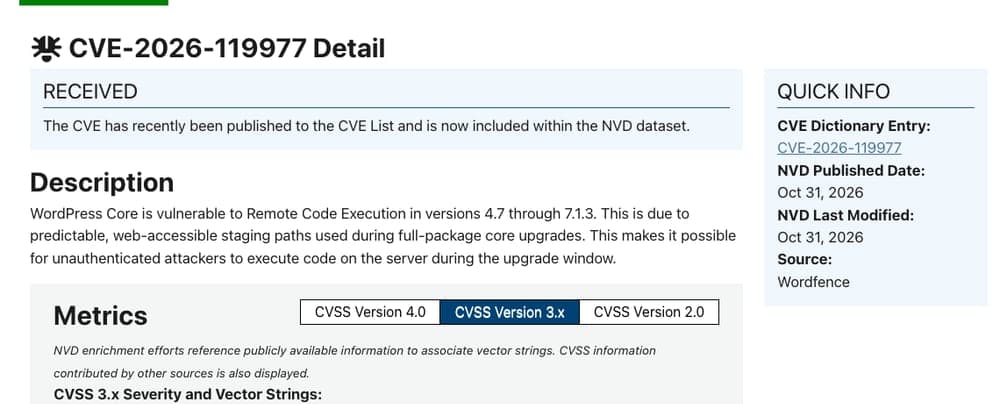
WordPress core 4.7 through 7.1.3 uses predictable, web-accessible staging paths during full-package upgrades, letting an unauthenticated attacker run code on the server while an upgrade is in progress.

The exposure happens during the fix itself, on a schedule attackers can guess.

Coverage of The WordPress upgrade window

Read on NVD

With Bastion

We probe the live site the way an attacker would. A staging path reachable from outside during an upgrade becomes a finding, with the request that reached it.

WooCommerce/CVE-2026-94361, CVE-2026-118184

Orders marked paid by anyone

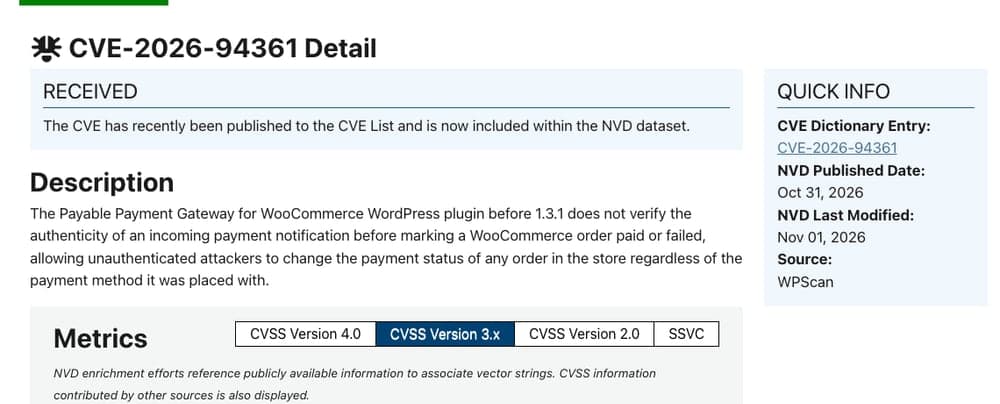
A WooCommerce payment gateway plugin did not verify incoming payment notifications, so anyone could mark any order in the store paid or failed. Fixed in 1.3.1.

A message nobody checks, a price the customer chooses. Scanners miss it because nothing is malformed.

Coverage of Orders marked paid by anyone

Read on NVD

With Bastion

We use the store like an attacker: forge the notification, change the price, and show you the order it produced. The fix arrives as a pull request that checks the sender.

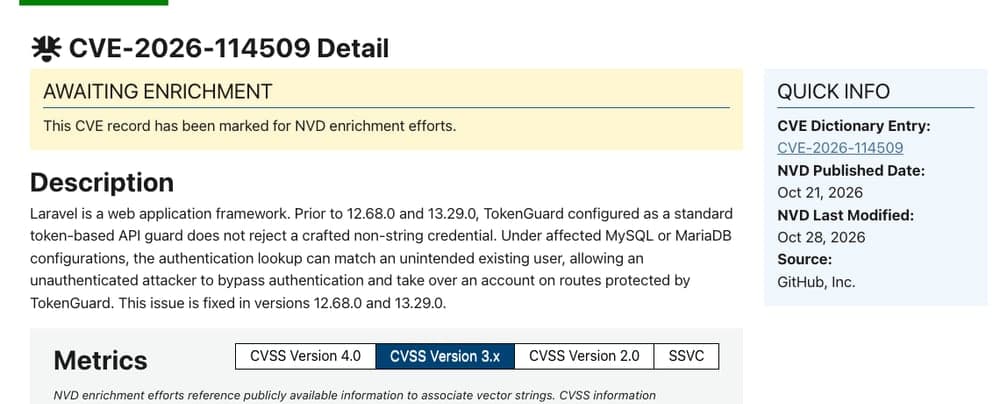
Laravel/CVE-2026-114509

Laravel token guard bypass

Laravel's TokenGuard did not reject a crafted non-string credential. On some MySQL and MariaDB configurations the lookup can match an existing user, so an unauthenticated request can take over an account. Fixed in 12.68.0 and 13.29.0.

The code looks right. Whether it's broken depends on the database behind it.

Coverage of Laravel token guard bypass

Read on NVD

With Bastion

We test the live API, not the repository, so a lookup that matches the wrong user on your database shows up as an account takeover. The fix: a pull request upgrading Laravel.

GitLab/CVE-2026-97229

GitLab regex RCE, exploited

A crafted regular expression in a CI configuration can let an attacker run code on a GitLab server (CVSS 10.0). CISA added it to its Known Exploited Vulnerabilities list.

A fix that exists isn't a fix that's running. A week was enough.

Coverage of GitLab regex RCE, exploited

Read on The Hacker News

With Bastion

We'd flag your GitLab as exposed from the day the fix shipped, and keep flagging it until the version answering requests is the patched one.

MongoDB/CVE-2025-14847

Databases that leak their memory

A flaw in MongoDB lets clients that never log in read pieces of the server's memory, which can hold data and credentials.

If your database answers strangers, it can leak what's in memory.

Seen this week

Actively exploited

CVE-2025-14847

With Bastion

We check whether any of your databases can be reached from outside and whether they answer without a login, then show you how to close it.

Cisco Secure Email/CVE-2025-20393

The email filter became the way in

Attackers are running their own commands on Cisco's email security gateway, the device meant to stop attacks.

Security devices face the internet too, and get attacked first.

Seen this week

Actively exploited

CVE-2025-20393

With Bastion

We test the devices you expose to the internet, the security ones included, the way an attacker would.

SAP NetWeaver/CVE-2025-31324

No login needed into the system that runs the business

An unauthenticated file upload in SAP NetWeaver's Visual Composer lets anyone place files on the server and run them.

The most important systems are often the oldest and the least watched.

Seen this week

Actively exploited

CVE-2025-31324

With Bastion

We find which of your business systems are reachable from outside and test them for exactly this kind of upload.

Langflow/CVE-2025-3248

AI tools left open to anyone

Langflow, a tool for building AI agents, ran code sent by anyone before version 1.3.0, with no login.

AI tooling gets deployed fast and left open.

Seen this week

Actively exploited

CVE-2025-3248

With Bastion

We find the AI tools you've deployed, check whether they're open to the internet, and attack them like any other app.

AI models and agents

New ways to talk agents out of their rules

Ways to trick AI models and agents into ignoring their instructions are being shared and refined.

Every new trick works on someone's agent first.

Seen this week

Exploits in development

With Bastion

We attack your agents with these techniques as they appear, and show which instructions and tools they can be talked out of.

Oracle E-Business Suite/CVE-2026-101767

Probing started days after the patch

Attackers began probing Oracle E-Business Suite for this flaw within days of the patch coming out.

The gap between a patch and an attack is now days.

Seen this week

Exploits in development

CVE-2026-101767

With Bastion

When a flaw like this is published, we check whether you run the affected version and whether it can be reached.

browser-use/CVE-2025-47241

Agents pushed past their allowed sites

browser-use, a library that lets AI agents browse the web, could be tricked past its list of allowed sites.

An agent's guardrails are only as good as the check that enforces them.

Seen this week

Exploits in development

CVE-2025-47241

With Bastion

We test the guardrails on your agents directly, including which sites and tools they can be pushed past.

Recent

Crypto exchange

$6B+North Korea takes more than $6 billion from Binance

On October 29 about $6.3 billion left Binance's wallets in roughly 20 minutes. Binance's first look points to a compromised engineer's laptop that may have reached the systems that sign withdrawals. The FBI says North Korea did it.

The way in was one trusted machine, not a bug in the exchange.

IT supplier

2,250One vendor's keys open 2,250 companies

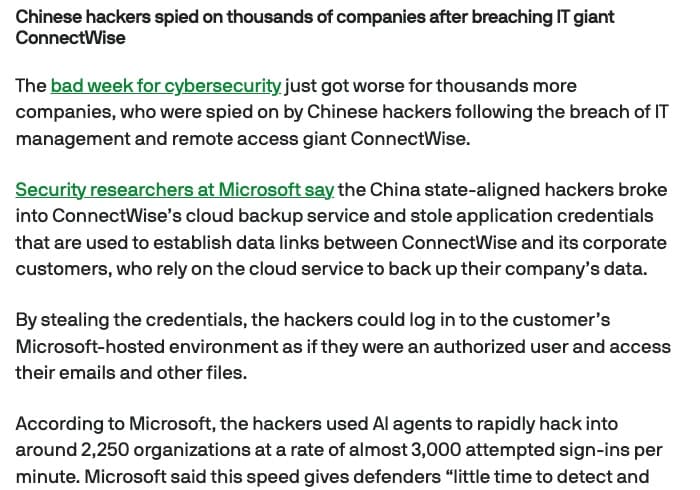
Hackers Microsoft ties to the Chinese state stole the credentials ConnectWise's backup service uses to connect to its customers. Using AI agents, they signed in to about 2,250 organizations' Microsoft environments at almost 3,000 attempts a minute.

A trusted supplier's key opened thousands of doors at once, faster than anyone could watch.

Insider

70+North Koreans on the payroll at 70 US companies

Prosecutors say North Korean operatives used stolen American identities to get hired remotely at more than 70 US companies, worked from company laptops kept in US “laptop farms”, took data and then extorted their employers.

The attacker had a job, a company laptop and a login.

Linux kernel/CVE-2025-21756

From inside one container to the whole server

Exploit work is under way on a Linux kernel flaw in vsock, which could let code running inside a system take it over.

One weak workload can become the whole machine.

Seen this week

Exploits in development

CVE-2025-21756